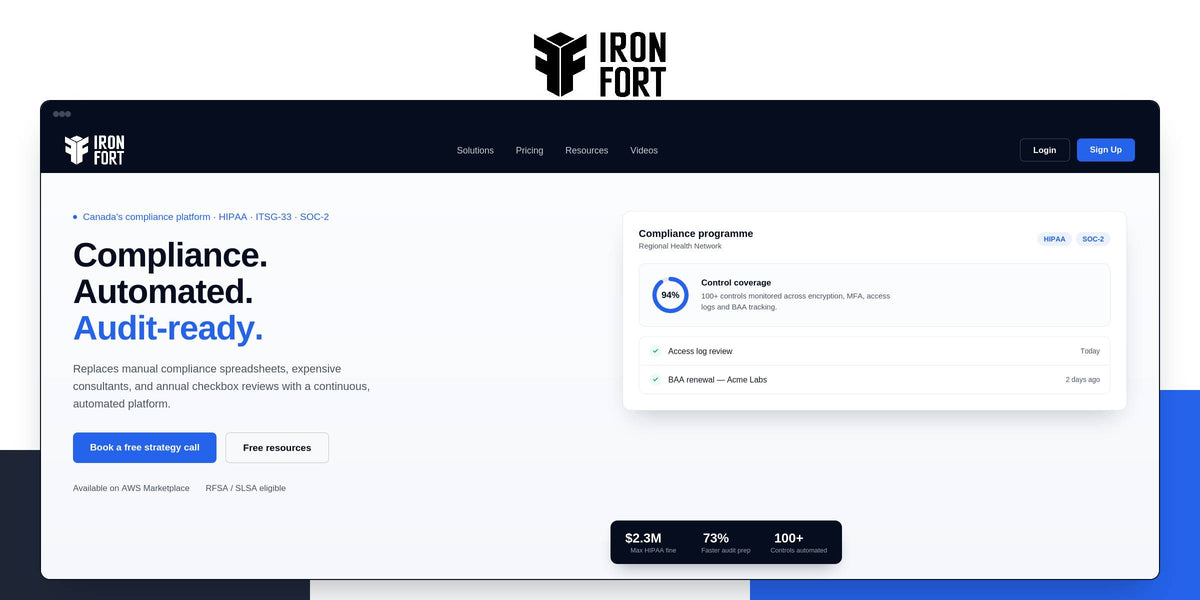
Need SOC 2 compliance without the cost and complexity of traditional audits?
Iron Fort automates compliance monitoring, evidence collection, and policy reviews so your team can stay audit-ready without spending months managing spreadsheets or relying on expensive consultants.
Built for SaaS companies, healthcare organizations, and Canadian government teams, Iron Fort helps you manage compliance continuously with AI-powered tools and framework-specific workflows.
-
Automate evidence collection: Gather, timestamp, and organize compliance evidence across 40+ integrations.
-
Identify risks faster: Use AI to score control gaps by severity and prioritize remediation.
-
Keep policies audit-ready: Analyze existing policies against SOC 2, HIPAA, and ITSG-33 requirements.
-
Simplify audit preparation: Generate organized audit packages on demand, without weeks of manual work.
-
Manage multiple frameworks: Map shared controls across SOC 2, and HIPAA to reduce duplicated effort.
Stop chasing evidence and start building a compliance program your team can maintain.
Get audit-ready with Iron Fort and simplify compliance from day one.

Automate SOC 2 compliance: Continuously monitor controls, identify risks, and prepare audit documentation without spreadsheet-heavy workflows.
Collect evidence automatically: Connect 40+ integrations, including AWS, Azure, Google Cloud, GitHub, and Microsoft 365, through read-only APIs with no agents required.
Manage multiple frameworks: Support SOC 2, HIPAA, ITSG-33 with AI-powered risk and policy analysis.
Stay audit-ready with expert support: Generate audit packages on demand, manage vendor risks and compliance records, and access compliance specialists according to your plan.
Why Iron Fort?
Iron Fort gives your team a smarter way to manage compliance by combining continuous monitoring, AI-powered analysis, and framework-specific automation in one platform, helping you reduce manual work, address risks earlier, and prepare for audits with greater confidence.
-
AI-powered risk analysis: Continuously assess SOC 2 controls, identify critical gaps, and generate a prioritized remediation roadmap.
-
Automated evidence gathering: Collect and organize timestamped evidence across your connected systems without manual tracking.
-
Framework-specific compliance: Access purpose-built workflows for SOC 2, HIPAA, and Canadian government ITSG-33 requirements.
-
40+ integrations: Monitor your cloud infrastructure, identity management, development tools, and business applications through read-only APIs, with no agents required.
-
Policy reviews that save time: Compare existing documentation against framework requirements and identify missing elements with clear explanations.
-
Multi-framework efficiency: Map overlapping controls across SOC 2 and HIPAA to reduce duplicate evidence collection.
-
Compliance expertise when you need it: Get access to SOC 2 and HIPAA specialists, with support options varying by plan.
-
AWS Marketplace availability: Purchase through AWS Marketplace and benefit from consolidated billing and potential credit eligibility.
How It Works
Step 1: Connect Your Environment
Integrate your cloud infrastructure, identity providers, development platforms, and other supported tools. Iron Fort scans connected systems through read-only APIs, without requiring agents.
Step 2: Monitor Controls Continuously
Iron Fort checks key security controls, including encryption, multi-factor authentication, access permissions, and backup policies, helping you identify issues as your environment changes.
Step 3: Identify and Prioritize Risks
Use the AI Risk Analyzer to evaluate control gaps by severity and build a prioritized remediation roadmap. Review existing policies with AI-powered analysis to identify missing requirements before your audit.
Step 4: Collect and Organize Evidence
The AI Evidence Gatherer automatically collects, timestamps, and organizes evidence from integrated systems. Keep documentation centralized and ready for review instead of chasing files across spreadsheets and tools.
Step 5: Prepare for Your Audit
Generate organized audit packages on demand, track training records and vendor risks, and maintain compliance documentation as your business evolves.
Key Features

-
AI Risk Analyzer: Continuously scores SOC 2 controls by severity, identifies critical gaps, and generates a prioritized remediation roadmap to help your team focus on the issues that matter most.
-
AI Evidence Gatherer: Automatically collects, timestamps, and organizes evidence across connected systems, reducing manual work and keeping documentation ready for audit preparation.
-
AI Policy Analyzer: Reviews existing policies against SOC 2 Trust Service Criteria and other supported framework requirements. Identify missing elements with plain-English explanations and access a library of 180+ SOC 2 policy templates.
-
Automated Control Scanning: Monitor security controls across 40+ integrations, including AWS, Azure, Google Cloud, Microsoft 365, GitHub, Okta, Microsoft Entra ID, Azure DevOps, and Cloudflare. Connect through read-only APIs without installing agents.
-
Multi-Framework Compliance: Manage overlapping controls across SOC 2 and HIPAA while reducing duplicated evidence collection. Iron Fort also supports ITSG-33 compliance for Canadian government requirements.
-
Live Security Monitoring: Run real-time checks on encryption, MFA, access controls, and backup policies across connected environments to help your team identify potential compliance gaps.
-
Vendor Risk Management: Automate annual vendor questionnaires, collect SOC 2 reports, and assess third-party risks with CC9.2-aligned risk scoring.
-
HIPAA Compliance Tools: Manage Business Associate Agreements with expiry alerts and completeness scoring, track workforce training and attestations, and document incident response workflows with notification timelines.
-
All Five SOC 2 Trust Service Criteria: Support compliance activities across Security, Availability, Confidentiality, Processing Integrity, and Privacy.
-
Audit-Ready Reporting: Centralize compliance evidence and documentation, generate audit packages on demand, and use Power BI dashboards for executive-level compliance reporting.
-
Canadian Government Compliance Expertise: Access purpose-built ITSG-33 workflows informed by Canadian government security requirements, including Protected A and B classification considerations and the Security Assessment and Authorization (SA&A) lifecycle.
-
AWS Marketplace Availability: Purchase Iron Fort through AWS Marketplace with consolidated billing and potential eligibility for applicable AWS credits.
Who's Iron Fort Best For?
Iron Fort is built for organizations that need to demonstrate security, manage compliance requirements, and prepare for audits without creating an administrative burden.
-
Early-stage and growth-stage SaaS founders: Prepare for SOC 2 requirements and remove compliance bottlenecks that can slow enterprise sales.
-
B2B software and engineering teams: Respond to enterprise security questionnaires and maintain evidence across your technology stack.
-
Startups pursuing SOC 2 Type I or Type II: Organize controls, policies, and evidence from the beginning of your compliance journey.
-
Lean security and compliance teams: Automate recurring tasks without needing to build a large internal compliance department.
-
Healthcare and health SaaS companies: Manage HIPAA-related policies, training records, Business Associate Agreements, and incident response documentation.
-
Companies in regulated or security-conscious industries: Support enterprise requirements across fintech, HR tech, legal tech, EdTech, and cloud infrastructure.
Testimonials
